

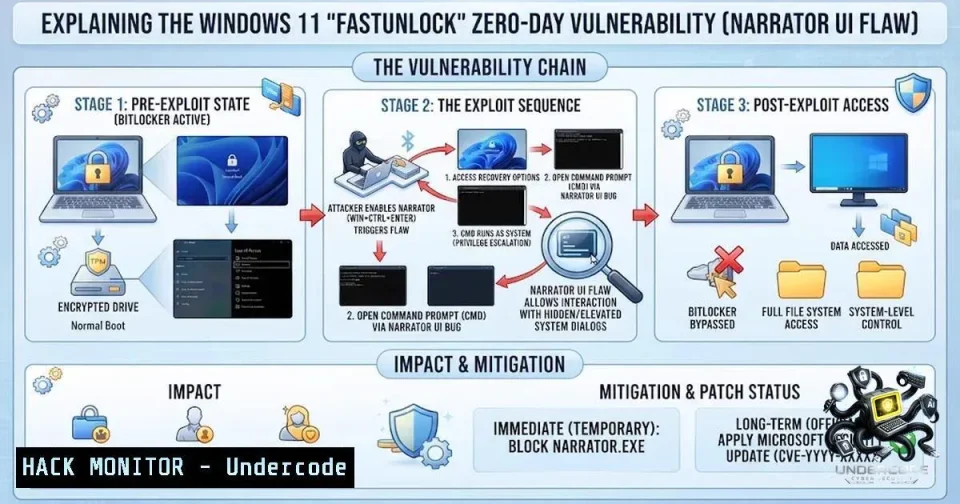
On November 19, 2026, security researcher Chaotic Eclipse published FastUnlock, a new Windows zero‑day that exploits the Narrator accessibility feature to bypass the lock screen and — the researcher says — undermine BitLocker protection. Chaotic Eclipse claims the exploit allowed code execution in the lock‑screen WsiAccount and that he breached a fully encrypted Windows 11 26H2 system with November security updates installed in five minutes.
FastUnlock: how the exploit works
According to the researcher, the attack requires physical access to the target machine and at least one user account linked to an online account. It starts from the Microsoft account recovery screen (the “I forgot my PIN” or password option). Enabling Narrator reportedly causes it to focus a hidden background window; by navigating Narrator’s options with the keyboard, an attacker can open Narrator’s settings and then follow several paths that can lead to code execution under the WsiAccount user.
Chaotic Eclipse describes one path that reaches File Explorer through the Bluetooth & Devices and AutoPlay settings. “Now I didn’t show the full code execution demo because I don’t really have a USB stick but I already did this enough times to know what happens next, your next step is to plugin a USB stick, as soon as you do, narrator will focus on explorer showing your mounted storage content and you can just navigate with the same button combination (CAPS LOCK + Arrow keys/Enter/Space), if you do everything properly the binary in your USB stick will be executed in the context of \”WsiAccount\”” the advisory reads.
The researcher says the root cause was introduced when Microsoft redesigned Narrator and failed to prevent the new interface from running in the lock‑screen account context. He characterizes the issue as consistently reproducible on the machines he tested and notes it is easier to exploit than previous lock‑screen bypass flaws: “It took a total of 5 minutes from finding this to breaching a fully encrypted bitlocker machine with Windows 11 26H2 November Patch installed, an issue caused by total negligence from Microsoft’s side… The vulnerability seems to be extremely consistent in every machine I tested it in, in other words, if you know how to control narrator in the background properly or just press the correct combination of buttons, you will get code execution in the target machine as well.” He adds: “I have not checked other windows versions so I am not really sure if this might work on windows 10.”
Researcher background and prior disclosures
Chaotic Eclipse, also known by aliases INFINITE NIGHTMARE, MSNightmare and Nightmare‑Eclipse, is known for publicly releasing proof‑of‑concept exploits for zero‑day vulnerabilities and for criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products and some have later been exploited in the wild. Notable previous disclosures include the Undefend and RedSun Defender zero‑days.
In September, the researcher released BigDiskBuster, a zero‑day he said triggers a denial‑of‑service vulnerability in Windows Defender Update. In the same month he released multiple zero‑day exploits targeting Nvidia (GreenSection) and Microsoft Defender (ShieldCrash). He also published exploits affecting other security products: HardBreacher, a claimed privilege escalation against Kaspersky Endpoint Security that the researcher said can create a DLL in System32 and may require repeated attempts; PrettyPrague, a privilege escalation targeting GenDigital Avast Antivirus; and FalconFlank, a privilege escalation targeting CrowdStrike Falcon.
Chaotic Eclipse recently revealed his name as Abdelhamid Naceri and said he previously worked for Microsoft in the UK and Germany. In a now‑deleted X post he described his departure, claiming Microsoft terminated his employment without a clear reason and that he rejected settlement offers because he wanted a formal explanation and assistance staying in Germany. He said he challenged the dismissal in a German labor court, that Microsoft changed its arguments during the case, and that the court ultimately upheld the termination. According to his account, the dispute left him with almost no compensation and caused serious financial and emotional problems, including treatment in a psychiatric hospital. He also admitted that an earlier claim that Microsoft had taken legal action against him was fabricated.
Chaotic Eclipse’s pattern of releasing working exploit code has fueled debate over responsible disclosure and the risks of publishing PoC exploits. The FastUnlock advisory and accompanying claims are the latest in a series of public disclosures by the researcher.
